Policy draft for review
Work within your authority
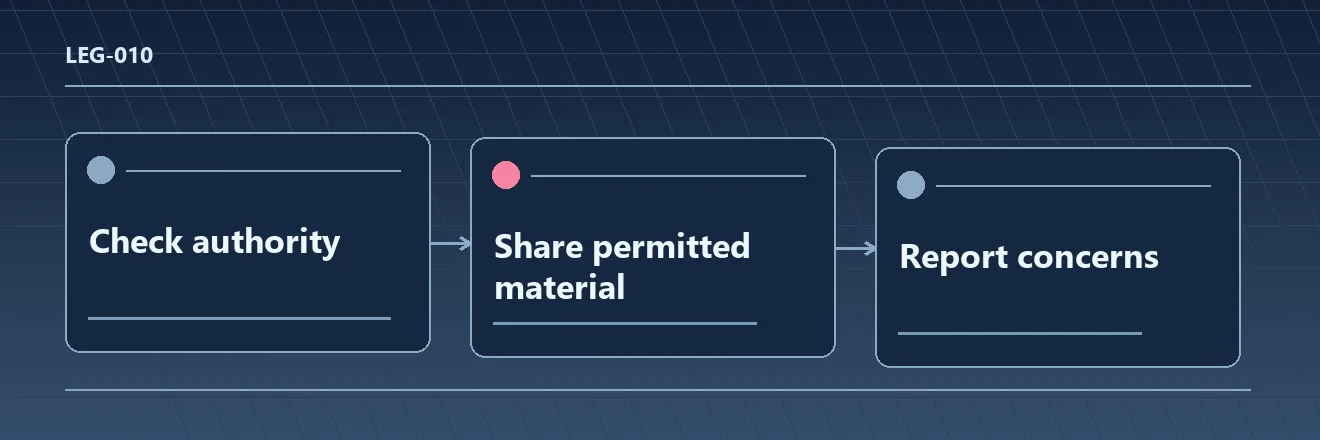
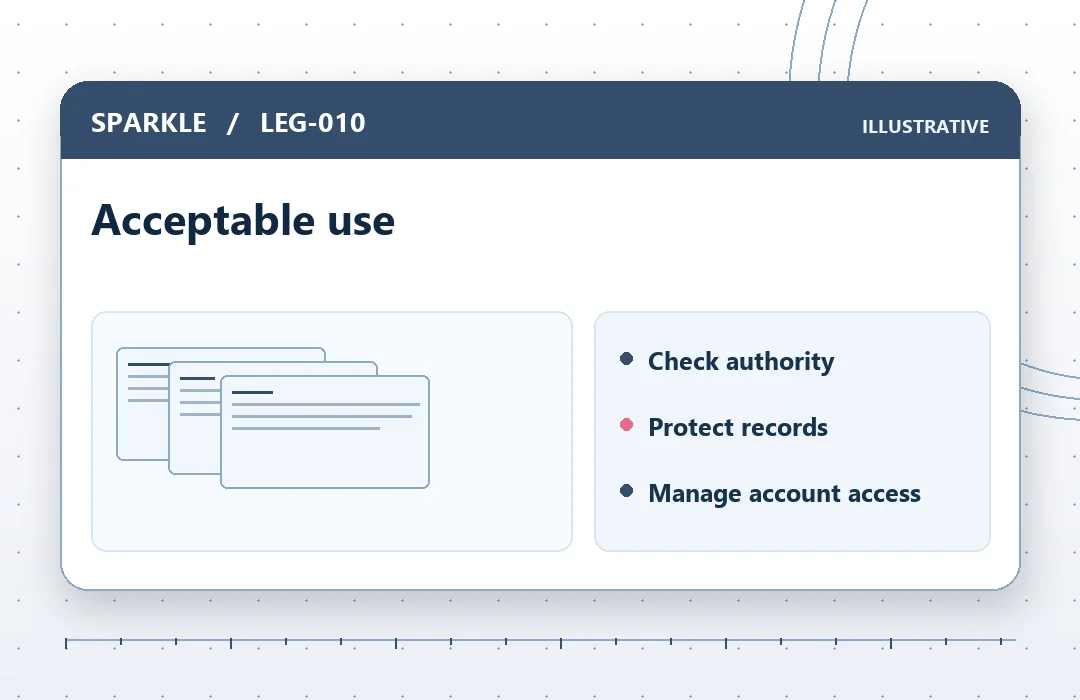
Provide only information, content and access that you are entitled to share. Give accurate instructions and identify restrictions before work begins. If a request depends on somebody else’s account or system, obtain the relevant permission and agree a suitable access method.
Protect systems and records
The website and services must be used lawfully. Prohibited uses include fraud, deception, unauthorised access and infringement of rights. Keep credentials and identification documents out of open forms. For work that requires sensitive information, use only the necessary material and the agreed secure channel.
Resolve concerns
We may seek clarification or suspend affected work if permission is missing or an instruction appears unlawful. The facts and written engagement guide the next step. At handover, review how access will be removed. Report suspected misuse to the company contacts published on this site.
Further information
Keep accounts under the organisation’s control and agree how permissions will be removed. Where a provider or external partner is involved, use the channel agreed with the supplier before sharing data or access.
Access at handover
Keep accounts under your organisation’s control. Agree how access will be removed or transferred when work finishes. If an approved external provider is involved, confirm the agreed route before sharing private documents or links.